Authentication & Cryptographic Security
Production-grade mock authentication loops with HMAC-SHA256 signed JWTs, copy-on-write profile updates, atomic token rotation with reuse detection, and 4-tier RBAC permission enforcement.
HS256
HMAC-SHA256 tamper-evident15m / 7d
Access vs Refresh TTL4 Roles
Admin, Editor, Viewer, GuestAtomic
Automatic reuse invalidation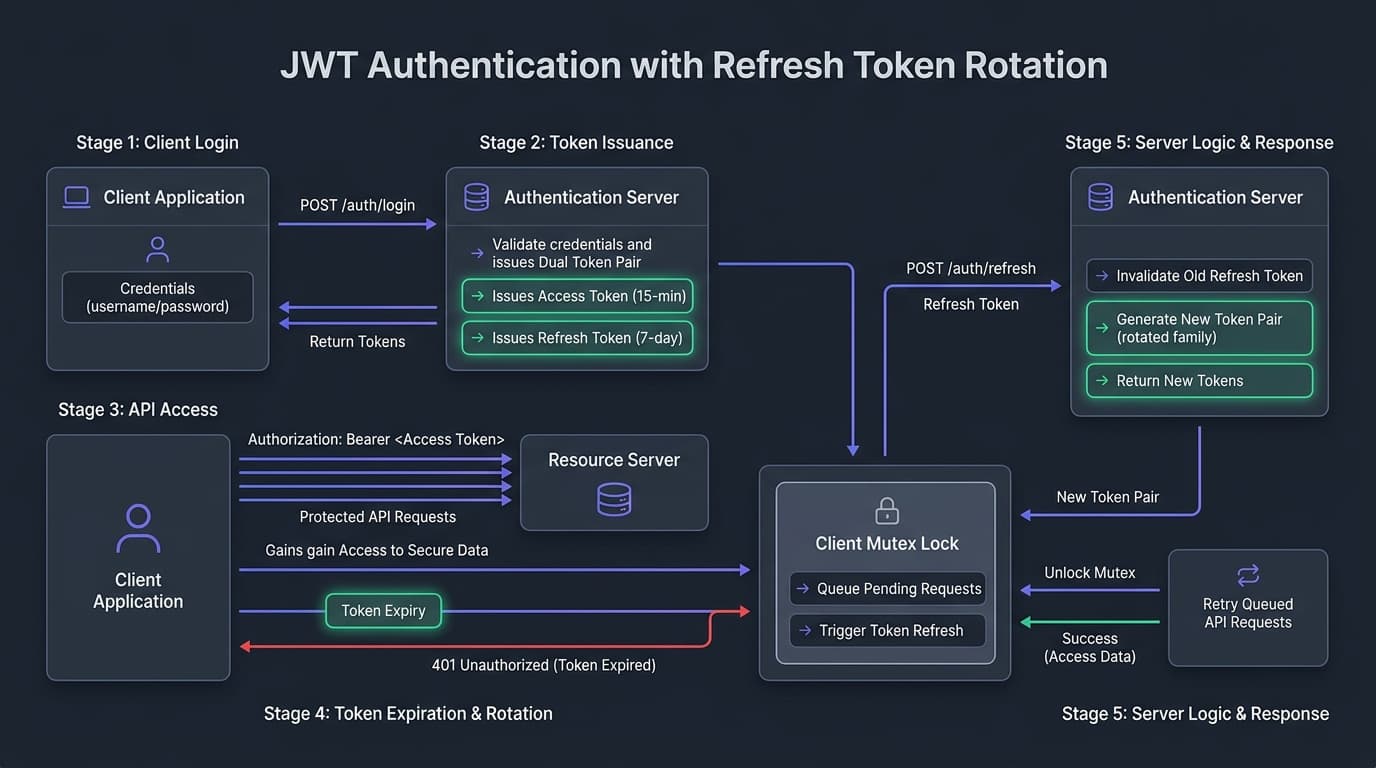
Login & Token Issuance
Submitting credentials issues a 15-minute access token and a 7-day refresh token pair.
Protected API Access
Client sends Bearer token. When expired, API responds with 401 Unauthorized.
Mutex Lock & Token Rotation
Client queues parallel requests, calls /auth/refresh, rotates token family, and retries.
Authentication Modules & Test Guides
Select a specialized security guide below to explore interactive testing playgrounds, token decoders, and code interceptors:
JWT Authentication Flow
Dual-token access & refresh authentication flow. Issue HMAC-SHA256 signed access tokens with custom TTLs, verify claims, and authenticate protected routes.
Refresh Token Rotation
Silent token refresh with automatic rotation. Guards against token reuse attacks and handles parallel 401 request storms with concurrency mutex locks.
RBAC Permission Matrix
Role-Based Access Control and granular scope matching. Test Admin, Editor, Viewer, and Guest personas with simulation headers and 403 Forbidden checks.
Expiry Simulation
Simulate instant or ultra-short token lifetimes (5s, 10s, 1m) without waiting. Test frontend auto-refresh interceptors and session timeout UX.
Clock Skew Drift
Model distributed clock drift (+120s, -60s) between client devices and authentication servers to validate token acceptance tolerance windows.
Password Recovery Loop
Full password reset workflow. Trigger forgot-password requests, inspect single-use recovery tokens in your virtual email inbox, and submit new passwords.
Dual-Mode Sandboxing
Understand how Playground API combines visitor session sandboxes with user-level overlays for multi-tenant simulation without seed cross-talk.
Built-in Personas & Test Credentials
Use these built-in test personas to immediately test authentication, token issuance, and RBAC authorization without registering custom accounts:
| Role Tier | Username | Password | Default Scopes | Capabilities | |
|---|---|---|---|---|---|
| admin | admin | admin@example.com | Password@123 | * | Unrestricted full access to all resources and destructive operations |
| editor | editor | editor@example.com | Password@123 | *:read, *:write | Can read, create, and update records; 403 Forbidden on delete and reset |
| viewer | viewer | viewer@example.com | Password@123 | *:read | Strict read-only permissions; 403 Forbidden on any POST, PUT, PATCH, DELETE |
| guest | anonymous | guest@example.com | - | public:read | Unauthenticated public visitor; 401 Unauthorized on protected resources |
REST Authentication API Reference
Complete specification of all available authentication, profile management, and RBAC discovery routes:
| Method & Path | Required Auth | Operation | Description |
|---|---|---|---|
| POST/api/v1/auth/login | None (Public) | Authenticate & Receive Tokens | Authenticate with username/email & password. Returns 15-minute access token and 7-day refresh token. Supports token_ttl and simulation headers. |
| POST/api/v1/auth/register | None (Public) | Register Custom Mock User | Create a new user record in your session overlay and receive immediate signed JWT auth tokens for testing signup workflows. |
| POST/api/v1/auth/refresh | Refresh Token | Rotate Refresh & Access Tokens | Exchange a valid refresh token for a fresh access token. Employs token family rotation; consumed tokens trigger REFRESH_TOKEN_REUSED (401). |
| GET/api/v1/auth/me | Bearer <token> | Get Current User Profile | Verifies the Bearer JWT access token and returns the current authenticated user profile, assigned role, and granular scopes. |
| PATCH/api/v1/auth/me | Bearer <token> | Update Current User Profile | Applies partial profile updates (name, email, bio, website) for the authenticated user. Diffs persist within your session overlay. |
| GET/api/v1/auth/roles | None (Public) | Get Supported Roles & Personas | Discovery endpoint returning all built-in RBAC roles (admin, editor, viewer, guest), persona credentials, and default capability scopes. |
| GET/api/v1/auth/permissions | None (Public) | Get Granular Permission Matrix | Returns the system permission matrix, allowed HTTP verbs per role, and wildcard matching syntax (*:read, posts:*). |
| POST/api/v1/auth/forgot-password | None (Public) | Request Password Reset Link | Dispatches a password recovery token and branded HTML reset link to the simulated virtual mailbox (/inbox/messages). |
| POST/api/v1/auth/reset-password | Reset Token | Confirm New Password | Submits a recovery token with the new password. Invalidates previous tokens and confirms updated password credentials. |
Interactive Auth Request Runner
Execute live requests directly against the authentication endpoints:
Register New Mock User (/auth/register)
Registers a brand-new user in your session sandbox overlay and returns immediate access & refresh JWTs:
Register Mock User
Update Authenticated Profile (/auth/me)
Apply partial attribute updates for the authenticated user. Pass your issued token in the Authorization header or rely on your active session cookie:
Update Profile Attributes
Roles Discovery (/auth/roles)
Inspect built-in personas, descriptions, and default scope arrays:
Query Supported Roles
Permission Matrix (/auth/permissions)
Retrieve the full granular action matrix and wildcard scope definitions: